Running the probe
The probe needs to be run from a shell terminal or command prompt
./reBop-probe
NAME:
   reBop-probe - Scan local drives for certificates and send them to reBop.
    Get and renew certificate from an ACME PKI (LetsEncrypt or other)

USAGE:
   reBop-probe [global options] command [command options] [arguments...]

VERSION:
   0.3.0

COMMANDS:
   scan
   scansend
   acme-cert
   help, h    Shows a list of commands or help for one command

GLOBAL OPTIONS:
   --help, -h     show help
   --version, -v  print the version
⚙️ Commands & Options
scan
CLI command to scan local path for certificates.
./rebop-probe scan [OPTIONS]
| Options | Description | Type | Default | Required? |
|---|---|---|---|---|
-p | path of the directory to scan | string | Yes | |
-o | output file path and name | string | Yes | |
-h | show command help | No |
The probe scans the provided path -p and stores the result in the file indicated with the -o option.
./rebop-probe scan -p ./ -o ./outfile
2021/03/23 09:00:23 [INFO] reBop-probe 0.4.0 started - scanning ./
Parsed 1 files
2021/03/23 09:00:23 [INFO] reBop scan Completed in : 6.36175ms
2021/03/23 09:00:23 [INFO] Parsed: 1 files
2021/03/23 09:00:23 [INFO] Found: 1 new files with certificate, 0 known files and 0 files without certificate
2021/03/23 09:00:23 [INFO] reBop file created:  ./outfile_rebop_2021-07-14.gz
In this example, the probe scanned a local folder and found 1 new certificate.
The output files contains this PEM encoded certificate as well as some information about the host such as hostname and ip addresses.
scansend
CLI command to scan local path for certificates and instead of writing the output to a file sends it directly to reBop.
./rebop-probe scansend [OPTIONS]
| Options | Description | Type | Default | Required? |
|---|---|---|---|---|
-p | path of the directory to scan | string | Yes | |
-h | show command help | No |
The probe scans the provided path -p and sends the result to the reBop server specified in the configuration file.
./rebop-probe scansend -p ./
2021/03/23 09:05:23 [INFO] reBop-probe 0.4.0 started - scanning ./
Parsed 1 files
2021/03/23 09:05:23 [INFO] reBop scan Completed in : 4.971209ms
2021/03/23 09:05:23 [INFO] Parsed: 1 files
2021/03/23 09:05:23 [INFO] Found: 1 new files with certificate, 0 known files and 0 files without certificate
2021/03/23 09:05:23 [INFO] Connecting to api.rebop.io:443 with API-Key
2021/03/23 09:05:23 [INFO] api.rebop.io:443 responded with 200 status code
2021/03/23 09:05:23 [INFO] reBop file [reBop-twxva.json] successfully sent
In this example, the probe scanned a local folder and found 1 new certificate. The result was successfully sent to reBop server.
acme-cert
CLI command to get or renew a digital certificate from the ACME PKI specified in the configuration file.
For this command to work:
acmepart of the reBop probe configuration file must be set.- because the probe implements HTTP and HTTPS challenge on TCP port 80 and 443 with the ACME PKI, it needs to be run with administrative privileges.
./rebop-probe acme-cert [OPTIONS]
| Options | Description | Type | Default | Required? |
|---|---|---|---|---|
-p | path to store new certificate | string | Yes | Yes |
-h | show command help | No |
The probe asks the ACME PKI a digital certificate for the hostname specified in the configuration file and sends it to reBop to be monitored.
Automation
The probe can be automated with a cron job or a Windows scheduled task.
Following is an example of a cron job executed every month. This script stops the Apache server, renew its digital certificate, sends it to reBop, installs it and restart the Apache server.
#!/bin/sh

sudo systemctl stop apache2
sudo ./rebop-probe/reBop-probe acme-cert /etc/ssl/tls-www/demo-certificate.rebop.io/
sudo systemctl start apache2
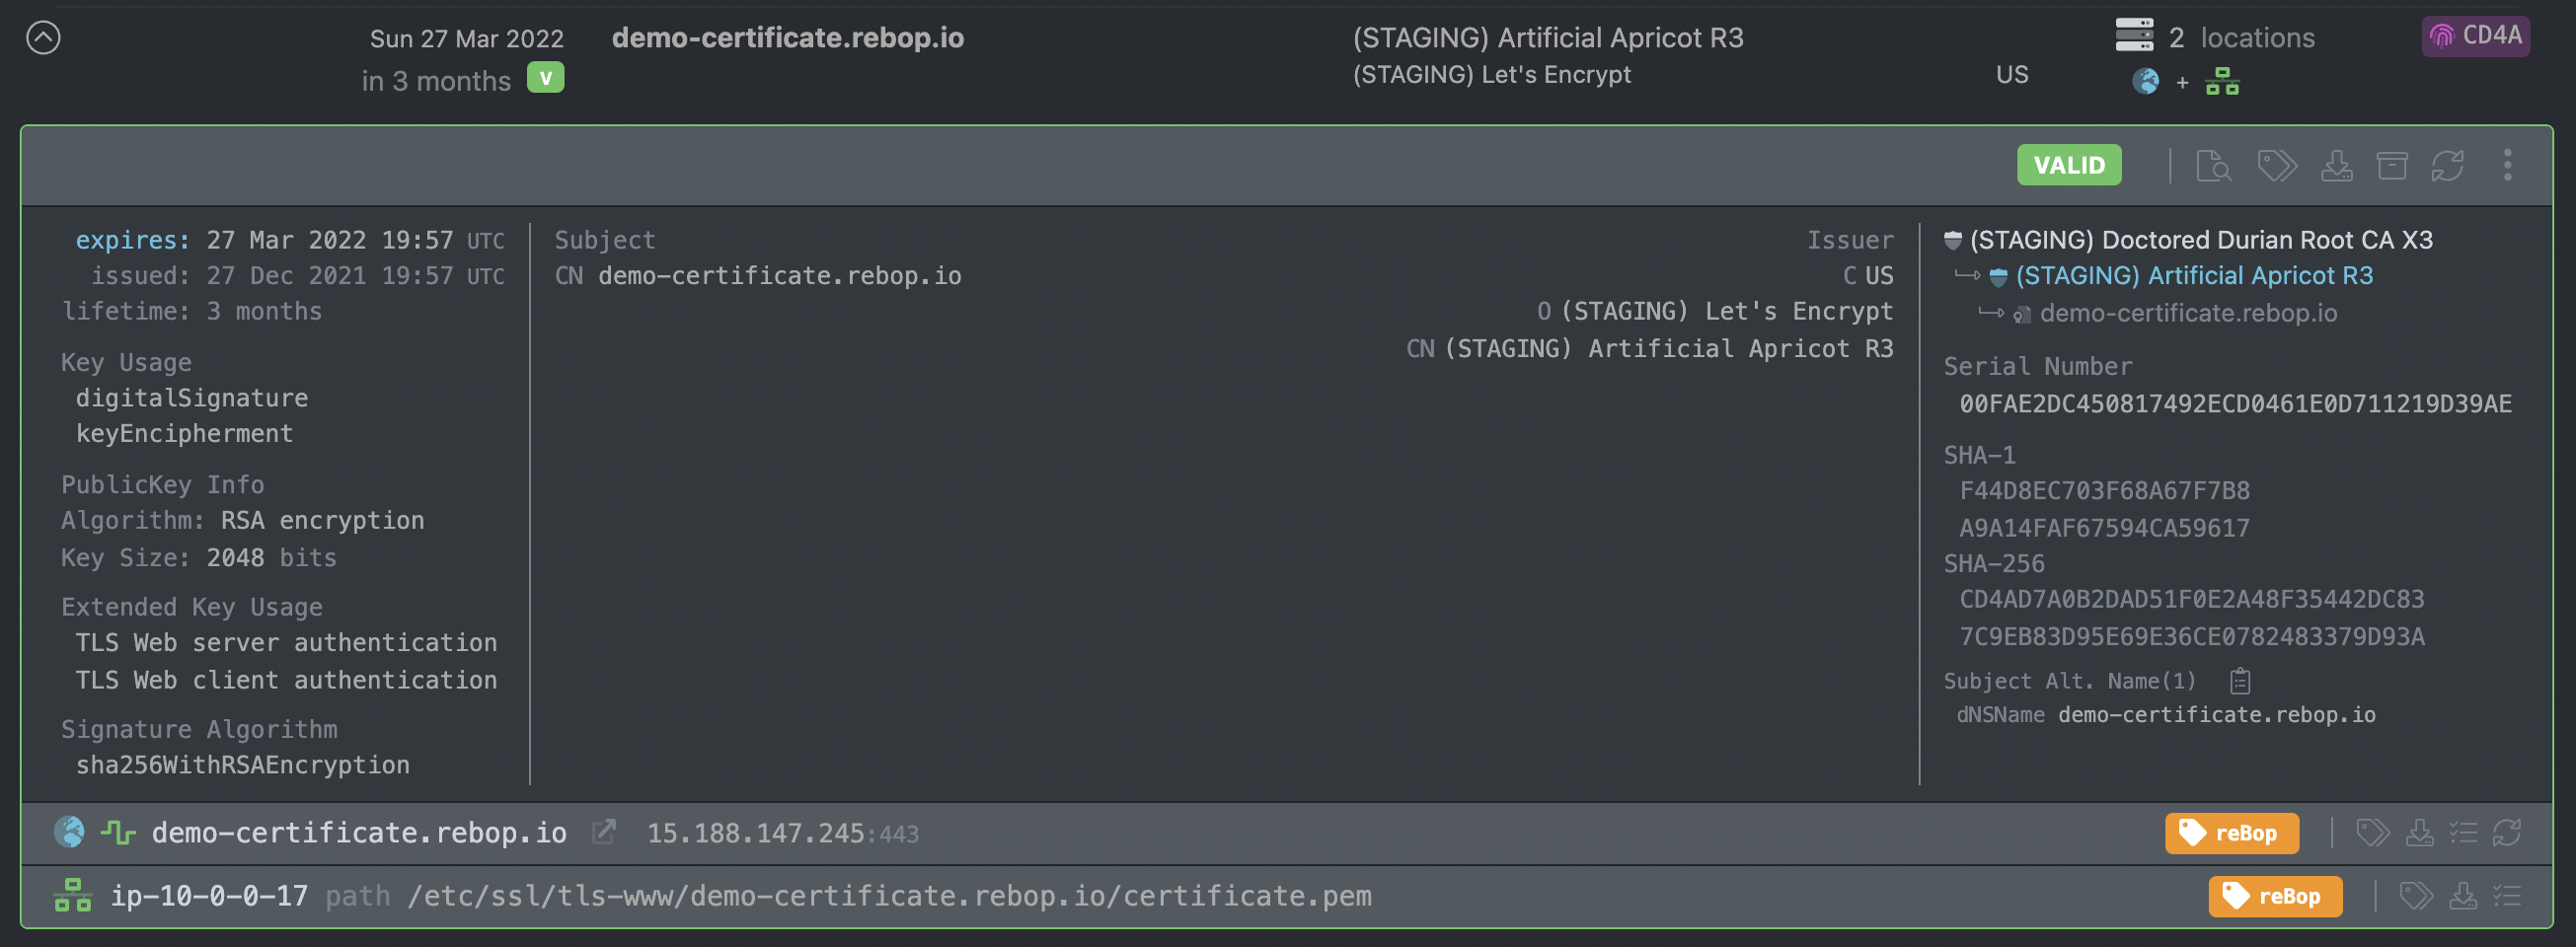
reBop will display this internet facing certificate in two locations:
- remote with its public IP address
- probe with its its local path